nuestra puntuaciónsin valoraciones de usuarios - valore →
Análisis de Tailscale (managed WireGuard mesh)
El estándar de oro para conectar tus propios dispositivos, y un pobre sustituto de una VPN para consumidores, tal como su nombre indica. Tailscale es un coordinador de red mesh WireGuard: el tráfico fluye de dispositivo a dispositivo con cifrado de extremo a extremo, el servidor de coordinación de código cerrado ve metadatos de dispositivos, claves y conexiones, incluyendo qué nodos se comunican entre sí, y los nodos de salida son tus propias máquinas a menos que pagues por el complemento de Mullvad. La capa gratuita Personal (6 usuarios, dispositivos ilimitados, verificada activa el 2026-11-02) es genuinamente generosa y las comunidades de homelab la adoran. Advertencias honestas: no hay auditoría pública del plano de control cerrado (los informes SOC 2 y Latacora están disponibles solo bajo solicitud), los registros del cliente se envían a Tailscale por defecto a menos que se desactiven, los pagos empresariales no son reembolsables según los términos, y la divulgación no coordinada de 'Tailworm' en octubre de 2026 (11 hallazgos SSH, escalada mediante reenvío de socket root, corregida en v1.104.4) mostró lo rápido que una herramienta de confianza puede requerir parches urgentes. Los usuarios que la alojan completamente en sus propios servidores escapan a la pregunta de confianza mediante Headscale, el servidor de control de terceros de código abierto, que Tailscale tolera más que apoya activamente. Calidad de los datos del expediente: todas las páginas del operador, archivos de GitHub, Wikipedia, la reseña independiente, noticias, el informe de Tailworm y archivos comunitarios fueron obtenidos en vivo por este sitio el 2026-11-02; el backend de coordinación en sí no puede ser verificado independientemente por nadie fuera de la empresa.
AuditoríaCódigo abierto3 señales de alertaHechos verified - operator pages (pricing, security, privacy policy, how-tailscale-works, exit-nodes docs, security bulletins, SSH investigation page, SSH findings blog, Series C blog), GitHub README + BSD-3 LICENSE + issue 498, Wikipedia, The Proof Desk review, Network World, Tailworm report, HN Algolia and Reddit arctic-shift archives all fetched live 2026-11-02; BleepingComputer and The Hacker News returned 403 (Cloudflare) and are cited from search-result snapshots only
October 2026 'Tailworm' incident: Cyberdione Labs published 11 findings in tailscaled v1.104.2 and headscale v0.29.5 with uncoordinated disclosure; root-privileged SSH Unix-socket forwarding could reach the Docker socket and tailscaled local API; fixed in v1.104.4 within days (fast response, but SecurityWeek and BleepingComputer noted a stolen device key stays valid until deleted at the control plane - reimaging the machine does not revoke it)
Five Eyes jurisdiction (Canada) plus a closed-source control plane: this is the whole argument for Headscale, NetBird or plain WireGuard if your threat model includes the operator itself
Heavy VC trajectory: $275M total funding and a $1.5B valuation (Bloomberg, 2025-04-08), first acquisition Border0 (2026-03-17, BetaKit/Bloomberg) and an enterprise pivot toward PAM and AI governance - the homelab product is now the top of a commercial funnel, though the free tier has so far been preserved and even widened (3 to 6 users in 2026)
Análisis
Borrador de Qwen3, verificado por la redacción de serviciovpn · Versión del análisis 3 · Texto actualizado 2026-11-02 · Hechos a fecha de 2026-11-02 · cómo verificamos
Nota de honestidad: no hemos hecho tests propios de Tailscale (managed WireGuard mesh) (fugas, velocidad, kill switch). Todo en esta página es metainvestigación basada en fuentes con enlaces fechados. En cuanto hagamos pruebas, los resultados aparecerán aquí y en el registro de cambios.
Overview
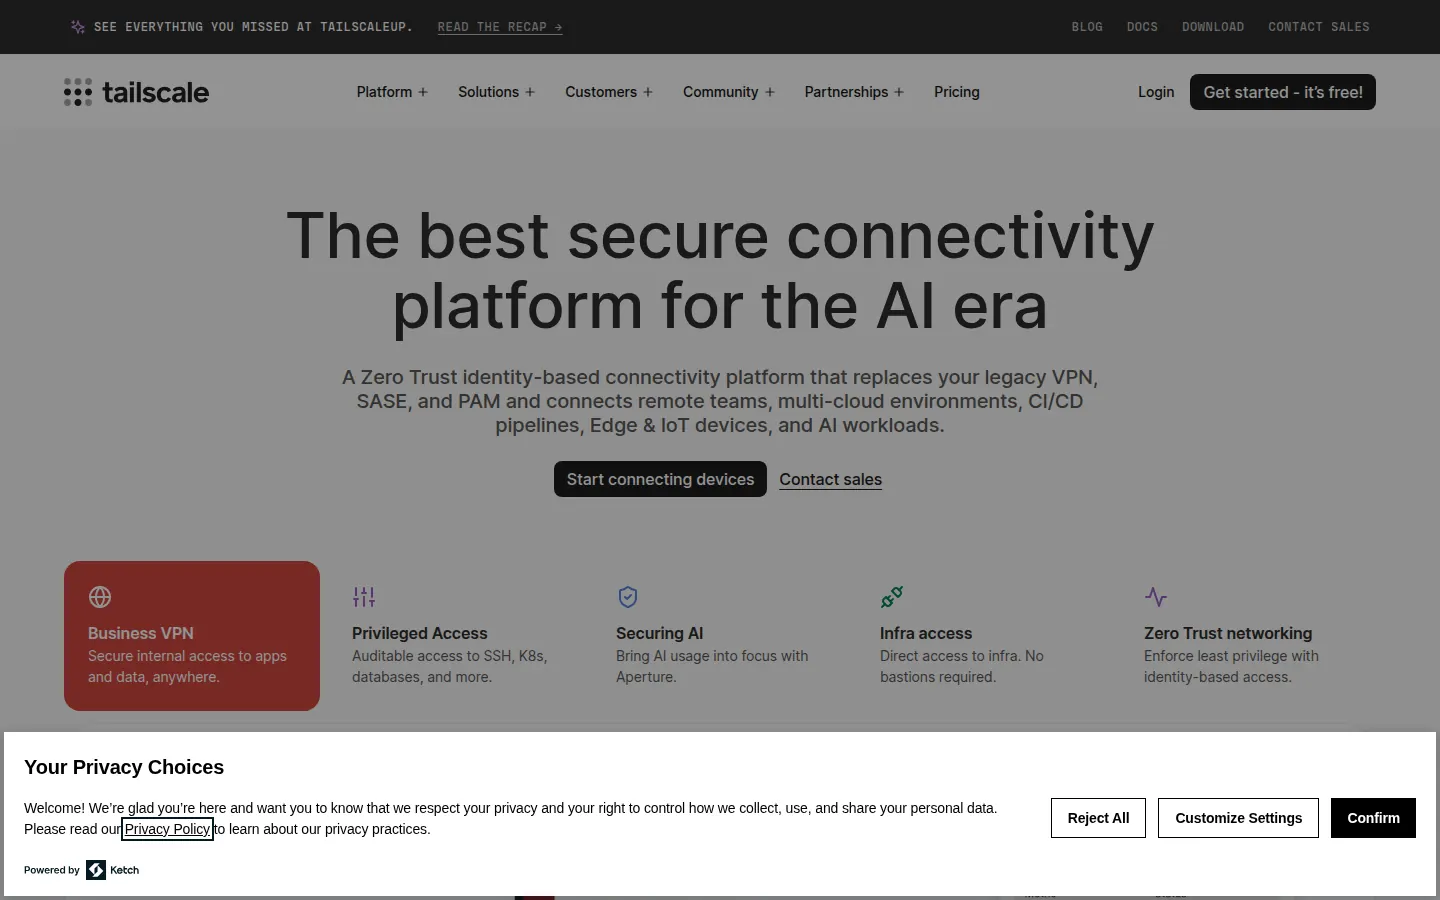
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29
Tailscale is a hosted WireGuard mesh coordination service that simplifies private network setup between your own devices. It’s not a consumer VPN - traffic stays end-to-end encrypted, but the closed-source control plane collects connection metadata. Operated by Tailscale Inc. in Canada (a Five Eyes country), it's ideal for self-hosters and remote access, but you must trust the operator with device and peer relationship data.
Logging & privacy
Tailscale claims it cannot see your traffic due to WireGuard’s end-to-end encryption, and DERP relay code is open source to verify they forward only ciphertext. However, the coordination server - closed source - collects metadata: device names, public keys, IP addresses, OS types, timestamps, and Inter-Node Traffic Logs showing which devices communicate and approximate data volumes. This is a "policy-only" logging claim with no public audit of the control plane. While SOC 2 Type II and Latacora audits exist, they’re available only on request. Jurisdiction in Canada raises concerns for high-risk users, and there’s no warrant canary.
Pricing & the renewal trap
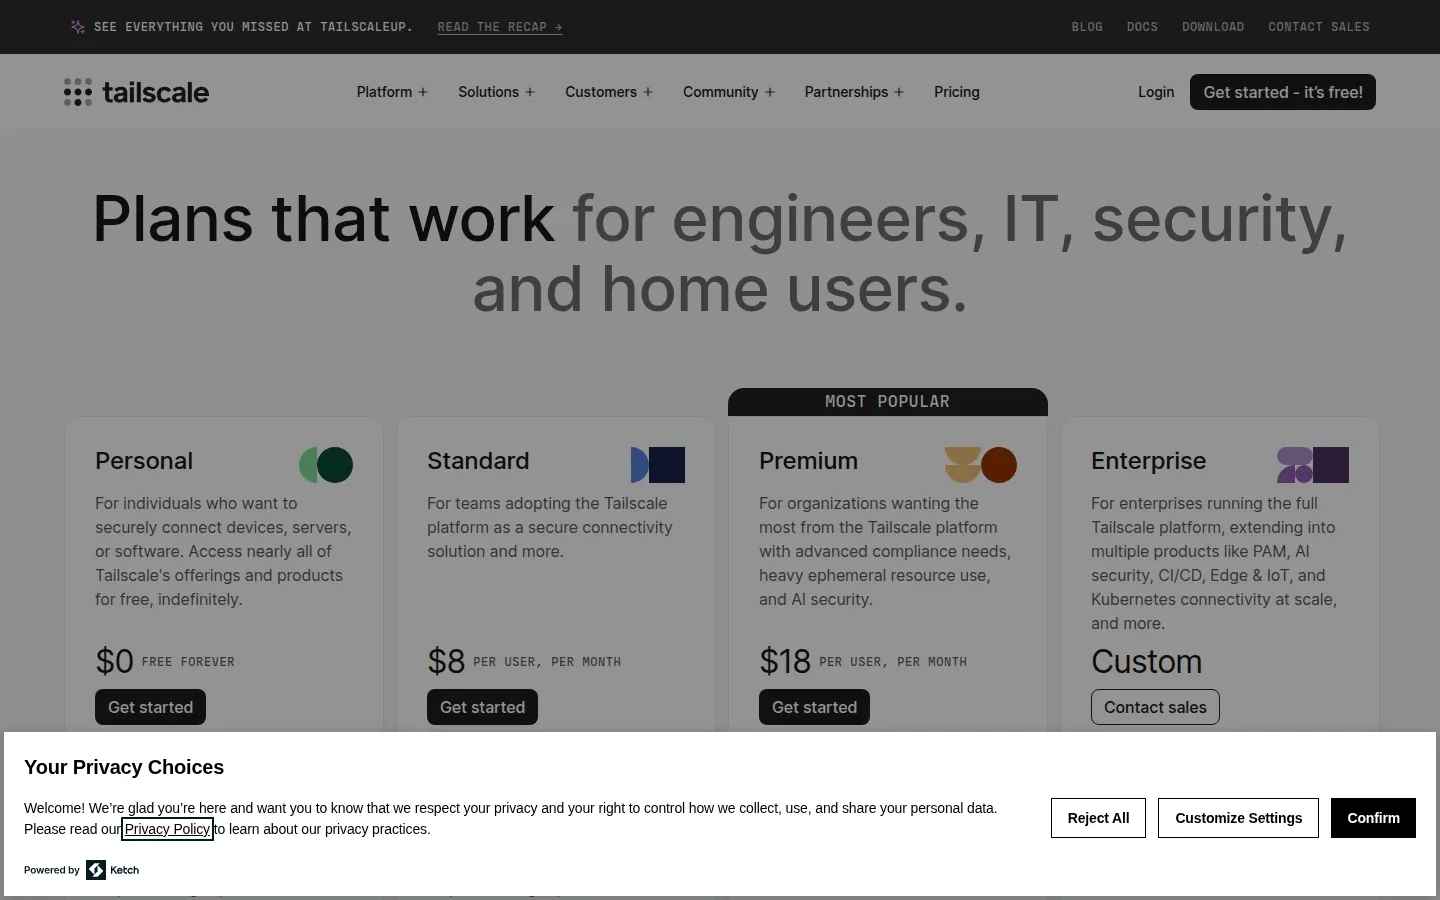
Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29
Tailscale’s Standard business plan costs $8 per user per month, with no change at renewal - the derived renewal ratio is 1. There’s no refund window (0 days), and payments are non-refundable per the Terms of Service. The free Personal plan supports up to 6 users and unlimited devices, verified live in 2026. No multi-year pricing or intro discounts exist, so the renewal trap is neutralized by flat pricing. Payment is fiat-only; crypto is not accepted.
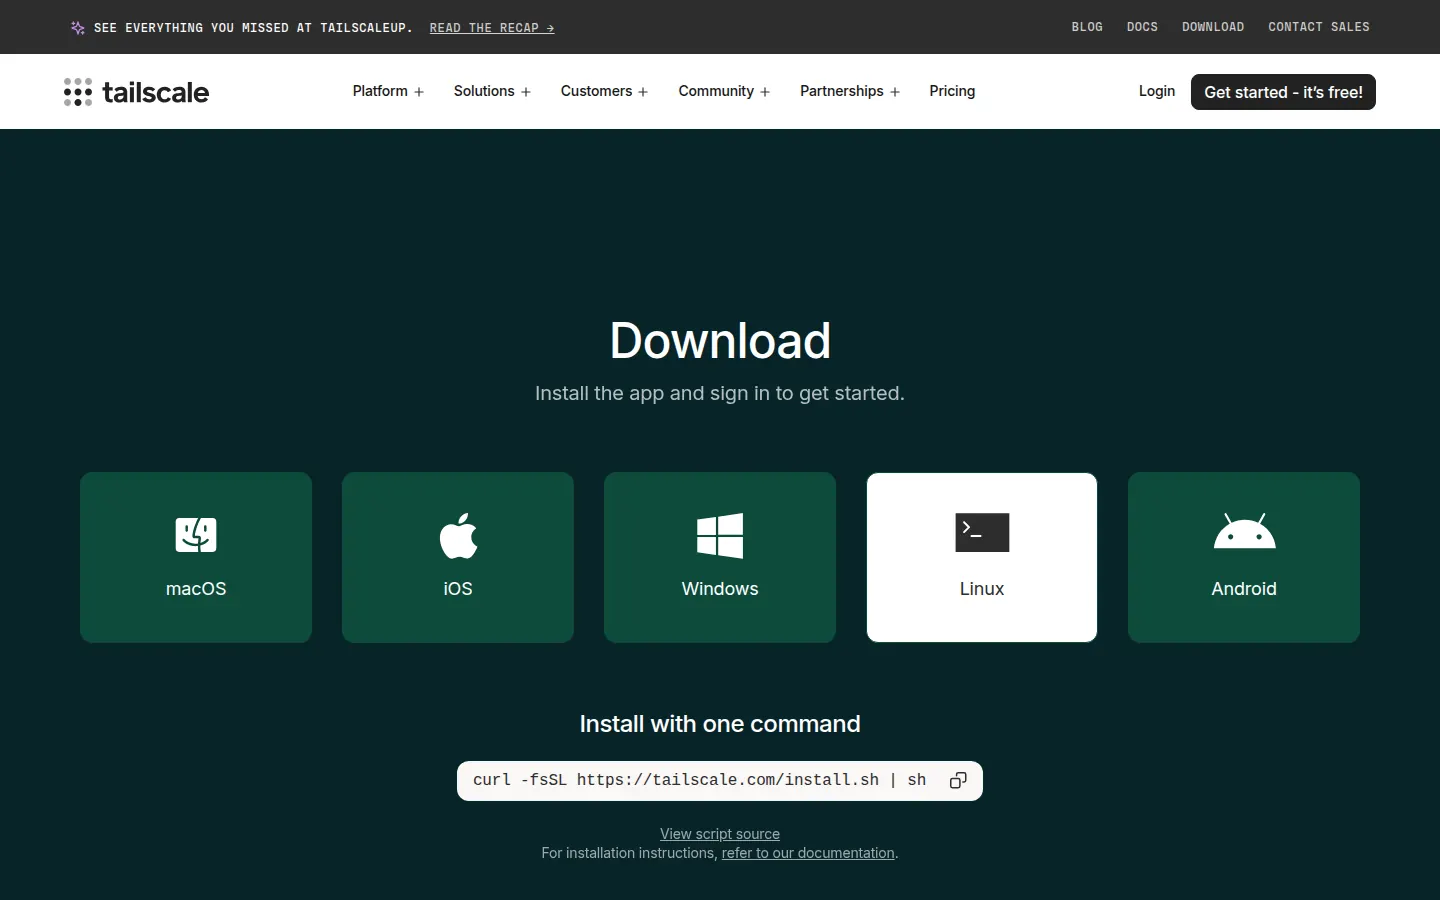
Built on WireGuard, Tailscale offers split tunneling, peer-to-peer routing, and optional exit nodes (your own devices or Mullvad add-on). It supports Windows, Mac, Linux, Android, iOS, and routers. No multihop, dedicated IPs, Tor over VPN, or obfuscation. Servers and countries count are irrelevant - this is a mesh, not a traditional VPN network. P2P is enabled by default; streaming geo-unblocking isn’t supported. No kill switch is documented. We haven’t run performance tests, but WireGuard ensures low latency when direct P2P works; DERP relays handle NAT traversal with minimal overhead.
Ownership & track record
Ownership details are not publicly disclosed. Tailscale Inc., based in Toronto, has raised $275M in funding and acquired Border0 in 2026, signaling an enterprise pivot. The 2026 "Tailworm" incident revealed 11 vulnerabilities, including root-level SSH escalation, though exploitation required prior access to an authorized device. Fixes shipped quickly, but the uncoordinated disclosure and lack of public audit for the control plane remain concerns. Data quality is verified across operator pages, GitHub, Wikipedia, and community archives, but the core coordination server remains unverifiable by independent parties.
Censorship resistance
Tailscale does not offer obfuscation and is not designed for use in heavily censored environments like China or Iran. Its reliance on direct UDP for WireGuard and DERP relays makes it easily detectable and blockable. Without traffic masking, this tool should not be used where circumvention of state-level censorship is required. Alternatives like Shadowsocks or obfuscated WireGuard setups are more suitable.
Verdict
Tailscale is the best choice for securely connecting your own devices with minimal setup - perfect for homelabs, NAS access, or remote work. It’s not a privacy tool for anonymity or streaming. You pay for convenience, not secrecy, and must trust Tailscale with metadata. The free tier is generous, pricing is flat, and the ecosystem is well-supported. No evidence suggests Tailscale pays review sites to promote it.
++ Qué se sostiene
Plan Personal gratuito: hasta 6 usuarios y dispositivos ilimitados, sin necesidad de tarjeta (página de precios vigente 2026-11-02).
Cifrado WireGuard de extremo a extremo; las claves privadas nunca abandonan los dispositivos; los retransmisores DERP solo reenvían texto cifrado (página de seguridad del operador obtenida 2026-11-02).
Clientes y código de retransmisor DERP de código abierto bajo licencia BSD-3, y una próspera ruta de autohospedaje de terceros mediante Headscale.
Sin fricciones: inicio de sesión con SSO, perforación NAT que funciona sin problemas, y la red privada sigue funcionando incluso cuando el servidor de coordinación está inactivo (documentación del operador).
El complemento de nodo de salida Mullvad a 5 $/mes por cada 5 dispositivos utiliza un operador respetado y verdaderamente sin registros.
Transparencia de seguridad: boletines de seguridad públicos al estilo CVE, y la respuesta a Tailworm en octubre de 2026 pasó de la divulgación a la versión parcheada en aproximadamente 4 días.
-- A qué prestar atención
El servidor de coordinación de código cerrado ve su inventario de dispositivos, IPs públicas y qué nodos se conectan con cuáles: la confianza en Tailscale Inc. es estructural.
No hay informe de auditoría público: las auditorías SOC 2 Tipo II y las continuas de Latacora están disponibles bajo solicitud o restringidas por cuenta.
No es una VPN de anonimato: no hay red de servidores alquilados, los nodos de salida son sus propios equipos, la transmisión y el desbloqueo geográfico están fuera de su alcance.
Los pagos son no cancelables y no reembolsables según los Términos de Servicio (obtenidos 2026-11-02).
Los registros de sesión del cliente se envían a log.tailscale.com por defecto, a menos que desactives esta opción con --no-logs-no-support
Expansión excesiva de funciones desde 2024 (PAM, puerta de enlace Aperture AI, filtrado DNS): voces de la comunidad advierten que el núcleo sencillo se está perdiendo bajo complementos empresariales
Prueba de realidad de precios
Precio inicial
8,00 US$ /user/mo · Renovación 8,00 US$/mes
Precio de renovación
8,00 US$/mes
Notas
Plan Personal gratuito para siempre (página de precios vigente 2026-11-02). Negocios: Estándar 8 $ por usuario/mes, Premium 18 $ por usuario/mes, Empresarial personalizado. Complementos: nodos de salida Mullvad 5 $/mes por cada 5 dispositivos, recursos etiquetados adicionales 1 $/mes cada uno. Términos de Servicio (obtenidos 2026-11-02): pagos 'no cancelables, no transferibles, no reembolsables'.
El flujo de dinero - lo que ganan los portales de análisis con esta recomendación
Estado de afiliación aún sin verificar
Si nos uniéramos a este programa, cada enlace de aquí llevaría rel="nofollow sponsored" y pasaría por /go/. Hasta entonces, nuestros enlaces apuntan directamente al sitio del proveedor, sin ningún rastreo. La lógica de ordenación no puede leer físicamente los campos de afiliación - aquí la prueba.
On the website
Captured by our screenshot bot from the live site (or its public archive). A capture is evidence of what the page showed at capture time - not an endorsement.
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29Tailscale (managed WireGuard mesh) apps / download page - live capture 2026-09-29
Antes de pagar: compruebe el precio de renovación, el plazo de reembolso y si un camino más barato o gratuito cubre su caso de uso - la lista honesta.
Estado de nuestras comprobaciones: 2026-11-02. Tailscale (managed WireGuard mesh) alcanza 4.9/10 en nuestro análisis ponderado. Hemos registrado 3 señales de alerta (listadas arriba). Los reportes de usuarios, la propiedad y el historial de incidentes están documentados con fuentes fechadas en el metaanálisis de abajo.
What do I actually get with Tailscale?
You get a managed WireGuard mesh that connects your devices securely with end-to-end encryption. The free plan allows 6 users and unlimited devices; business tiers add policy controls and support. Traffic flows peer-to-peer or via DERP relays, and exit nodes let your devices route through your own servers.
What is the renewal price and total cost over three years?
The monthly rate is $8 per user, with no change at renewal - the renewal ratio is 1. Since pricing is flat and recurring, the three-year cash total is not precomputed, but you’ll pay $8 per user each month indefinitely.
What proof is there for Tailscale’s no-logs claim?
There is no independent public audit of the closed-source coordination server. The logging claim is "policy-only" - Tailscale says it collects only metadata (device info, connection logs), but this can’t be independently verified. DERP relay code is open source and doesn’t log, and SOC 2 reports are available only on request.
Can I use Tailscale in a censored country like China or Iran?
No. Tailscale lacks obfuscation and uses standard WireGuard traffic patterns that are easily detected and blocked. It is not suitable for bypassing state-level censorship. Use tools designed for obfuscation, like Shadowsocks or customized WireGuard with cloaking.
Can I pay anonymously or sign up without an identity?
No. You must sign up using an email or SSO identity (Google, GitHub, etc.). True anonymity isn’t possible on the hosted service. For anonymous-adjacent use, self-host Headscale with a private auth backend or run plain WireGuard without a coordinator.
What happens if Tailscale shuts down or gets acquired?
If Tailscale shuts down, hosted users lose coordination. Self-hosted Headscale users remain unaffected. The client is open source (BSD-3), but the control plane is not. Acquisitions (like Border0) suggest enterprise focus, but the free tier has been preserved and expanded so far.
What’s the honest free or cheap alternative?
Use Headscale - a fully open-source, self-hosted Tailscale-compatible control plane - or plain WireGuard for full control. For consumer privacy, consider Mullvad (audited no-logs, flat pricing) or IVPN (independent, transparent). These cost money but don’t rely on trusting a closed coordinator.
El metaanálisis: lo que internet dice de Tailscale (managed WireGuard mesh)
No esperamos que nos crea. Este análisis es un metaanálisis: abajo verá lo que afirman otros portales de análisis - con sus conflictos de interés señalados -, lo que reportan los usuarios en Reddit y foros y quién opera realmente Tailscale (managed WireGuard mesh). Cada afirmación enlaza su fuente para que pueda comprobarla usted mismo.
Lo que dicen otros testers (1)
Cada fuente lleva una etiqueta de conflicto de nuestra base de datos de portales de análisis. «Financiado por afiliación» significa: la web gana si usted compra lo que recomienda. Las voces críticas las incluimos deliberadamente.
Fetched 2026-11-02: small independent editorial review (monetization unknown). Honest scoping: Tailscale is 'not a VPN in the sense most VPN reviews use the word'. Likes the generous free plan and E2E encryption; dislikes the closed-source coordination server that sees device-to-device metadata, client logs streaming to Tailscale by default, non-refundable payments, and no public audit report (SOC 2 on request). Verdict: easiest way to connect your own devices; wrong tool for hiding your IP or streaming.
Lo que dicen los usuarios (6)
Reddit, foros, HN - parafraseado y enlazado, nunca fuera de contexto. Anécdotas, no pruebas - pero las quejas de reembolso y los reportes de fugas son el mejor sistema de alerta temprana que tiene este mercado.
Fetched 2026-11-02 (25 comments): homelab texture - Plex/Jellyfin served over tailnets, subnet routers, Serve vs Funnel security advice, ephemeral-node Docker troubleshooting, awareness of the Tailscale SSH vulnerabilities via the official r/Tailscale post, distrust of third-party UIs.
Fetched 2026-11-02 (15 comments): Tailscale as the default way to close public exposure after Plex/Nextcloud zero-days; binding containers to tailnet IPs; 'Headscale can be used if you want 100% self-hosted'; one user moving public-facing services to SSO + Cloudflare instead.
Fetched 2026-11-02 (15 comments): r/VPN regulars recommend Tailscale exit nodes as the free way to get a home IP while traveling; one sarcastic 'beautiful disclosure' jab after the SSH patch; exit node on Apple TV or Pi suggested.
Thread page fetched 2026-11-02 (HTTP 200), comments via HN Algolia API: accurate framing that the flaws require an already-authorized tailnet peer, Headscale users affected too (bug in tailscaled), 'nearly everyone uses zero advanced features', plug for Headscale/NetBird, praise for the fast fix.
Fetched 2026-11-02 via GitHub API: the original community request to open-source the coordination server ('it would be even more perfect if the server was open-source'), opened June 2020, closed December 2022 without the server being open-sourced; the issue that seeded years of Headscale advocacy.
Fetched 2026-11-02 (9,881 comment hits for tailscale; 2,276 for headscale): HN treats Tailscale as core homelab/devops infrastructure - recommended by default, incident discussed with technical precision, Headscale normalized as the self-host answer.
Informe de hechos con IA - todo lo que sabemos, condensado
Generado por Qwen3 el 2026-11-02 a partir de nuestra base de datos de hechos y las fuentes enlazadas. Resume - no añade hechos. Contraste todo lo importante con las fuentes enlazadas.
Bottom line: Tailscale is the easiest way to connect your own devices securely via WireGuard, with a generous free tier (6 users, unlimited devices). It is not a consumer VPN and does not hide your IP from websites or provide anonymity. Traffic is end-to-end encrypted, but the coordination server sees metadata about which devices talk to which, including public IPs and connection patterns.
The logging truth: Tailscale claims it cannot read your traffic due to WireGuard encryption, which is accurate - payloads are safe. However, it admits to collecting device metadata, connection logs, and traffic statistics (Inter-Node Traffic Logs), stored in Canada, the US, Germany, and the UK. This metadata collection is confirmed in its privacy policy and security page; the closed-source control plane cannot be independently verified, and audits (SOC 2, Latacora) are not public.
Pricing reality: The Personal plan is $0 forever with solid limits (6 users, unlimited devices). Business tiers start at $8/user/month with no intro discount, and payments are non-refundable per the Terms. No billing traps beyond the hard renewal terms - pricing is flat and transparent, but you lose money if you cancel.
What reviewers say vs what users say: Independent reviewers like The Proof Desk stress Tailscale’s misclassification as a VPN, praising its encryption and free tier but criticizing the closed control plane and default client logging. Users on Reddit and HN overwhelmingly praise it for homelab and self-hosting use, though the October 2026 Tailworm incident sparked debate - some dismissed the risk (required prior access), while others questioned trust in the platform, showing a split between operational utility and security paranoia.
Who runs it: Tailscale Inc., based in Toronto, Canada, founded in 2019, operates the service. It has raised $275M and is pivoting toward enterprise identity and AI governance, acquiring Border0 in 2026. The company tolerates self-hosted alternatives like Headscale but keeps its control plane closed, making full trust unavoidable for hosted users.
Fuentes & cómo se hizo este análisis
Cada fuente externa usada en esta página, con su fecha de consulta y su clase de prueba [A]-[D] (A = fuente primaria/del operador, B = prensa seria/investigación, C = comunidad, D = mediciones propias). Metodología: cómo verificamos. Las fuentes desaparecen o cambian - si un enlace está muerto, avísenos por la página de contacto.
Evidence classes on this page:[A] A: 11[B] B: 8[C] C: 6[D] D: 0(D stays empty until our own test phase)
The most credible self-hosting on-ramp in the VPN space, built by and for people inside the censorship: the app is free and open source, you connect it to your…
auditadoCódigo abierto
Inicial: 5,00 US$ /mo
Cyprus (EUPHORIATECH LIMITED, Nicosia, reg HE 484287 per site footer, verified 2026-11-02; IP rights in Portugal with Amnezia LDA, ops in Estonia) - for self-hosted users the operative jurisdiction is wherever their own VPS is hostedvpn autohospedado hace 3 días
The incumbent of self-hosted business VPNs, and still a safe pick in 2026 - with one honest fork in the road. Access Server is the polished, supported way to…
AuditoríaCódigo abierto
Inicial: 7,00 US$ /mo
United States - OpenVPN Inc., Pleasanton, California (about page fetched 2026-11-03); a Five Eyes member countryvpn autohospedado hace 41 h
The most polished way to hand censorship-resistant access to people who cannot configure a VPN: a few clicks in the Outline Manager builds a Shadowsocks server…
AuditoríaCódigo abierto
Inicial: 3,00 US$ /mo
United States - Outline Foundation, 30 N Gould St. #57975, Sheridan, Wyoming (contact address in Terms of Service and on the Google Play developer listing); ToS governed by Wyoming law. The software itself has no jurisdiction: the operative jurisdiction for a self-hosted user is wherever their rented VPS is located and the laws governing their cloud provider.vpn autohospedado hace 2 días
Aún no hay comentarios - sea el primero. Publicar pasa por una breve prueba de trabajo en su navegador (antispam), sin necesidad de cuenta.